Keygraph - Continuous Agentic Pentesting for the Enterprise
Continuous agentic pentesting and AppSec for the enterprise. Autonomous exploits validated against your live app, inside your perimeter. Built by the Shannon team.
Introduction
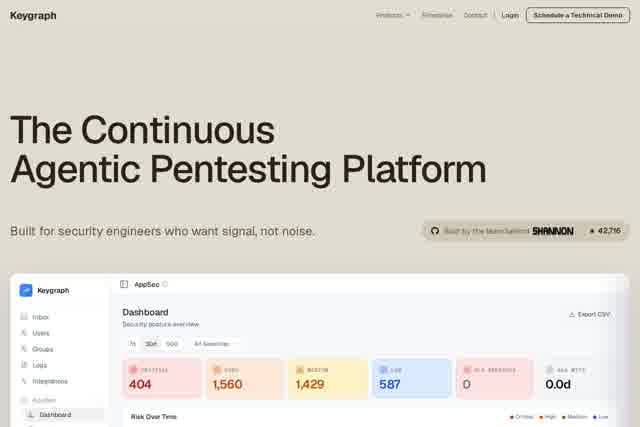
Keygraph is a next-generation enterprise-grade continuous security testing platform built by the Shannon team. It leverages autonomous agentic technology to perform automated penetration testing and vulnerability validation against real applications within your internal network environment. Unlike traditional security scanning tools, Keygraph simulates the behavior patterns of advanced attackers, automatically executing exploit attempts within controlled boundaries and delivering real-time security risk feedback. This product is designed for enterprises that require continuous, deep security validation, helping security teams discover and remediate critical vulnerabilities before an attack occurs.
Key Features
- Continuous intelligent penetration testing: Powered by autonomous agents, Keygraph runs around the clock to automatically probe and exploit vulnerabilities in enterprise applications without human intervention.
- Real validation inside your network: All testing is performed within your own network perimeter, ensuring data security and compliance while providing realistic attack paths and impact assessments.
- Autonomous exploit and verification: The system doesn't just report potential risks — it actively attempts to exploit vulnerabilities to confirm their real-world severity, eliminating false positives.
- AppSec workflow integration: Seamlessly connects with existing development and security toolchains, automatically generating remediation recommendations and priority rankings to accelerate vulnerability closure.
- Visual attack path analysis: Provides intuitive attack chain and asset relationship diagrams to help teams understand the full scope of risk.
Highlights
- Agentic architecture with intelligent decision-making: Unlike simple rule-based scanning, Keygraph's agents dynamically adjust attack strategies based on application responses, mimicking the mindset of real attackers.
- Low false-positive rate, high confidence: Every vulnerability report is backed by actual exploit validation, dramatically reducing time spent triaging false alerts.
- Secure and compliant with no data exfiltration: All testing is conducted inside the customer's network, so sensitive data never leaves the enterprise boundary, meeting strict security and privacy requirements.
- Built by the Shannon team: With deep hands-on offensive and defensive security expertise, the Shannon team ensures the product's reliability and effectiveness in complex enterprise environments.
Who It's For
Keygraph is built for enterprise security operations teams (SOC) who need continuous monitoring and validation of application security posture to reduce attack surface; DevSecOps engineers looking to embed automated security validation into development and release pipelines for higher delivery quality; penetration testers and red teams seeking efficient, repeatable automation to augment manual testing with greater depth and frequency; and security leaders and CISOs who need quantifiable, trustworthy security data to support risk decisions and compliance audits.