DeepTeam
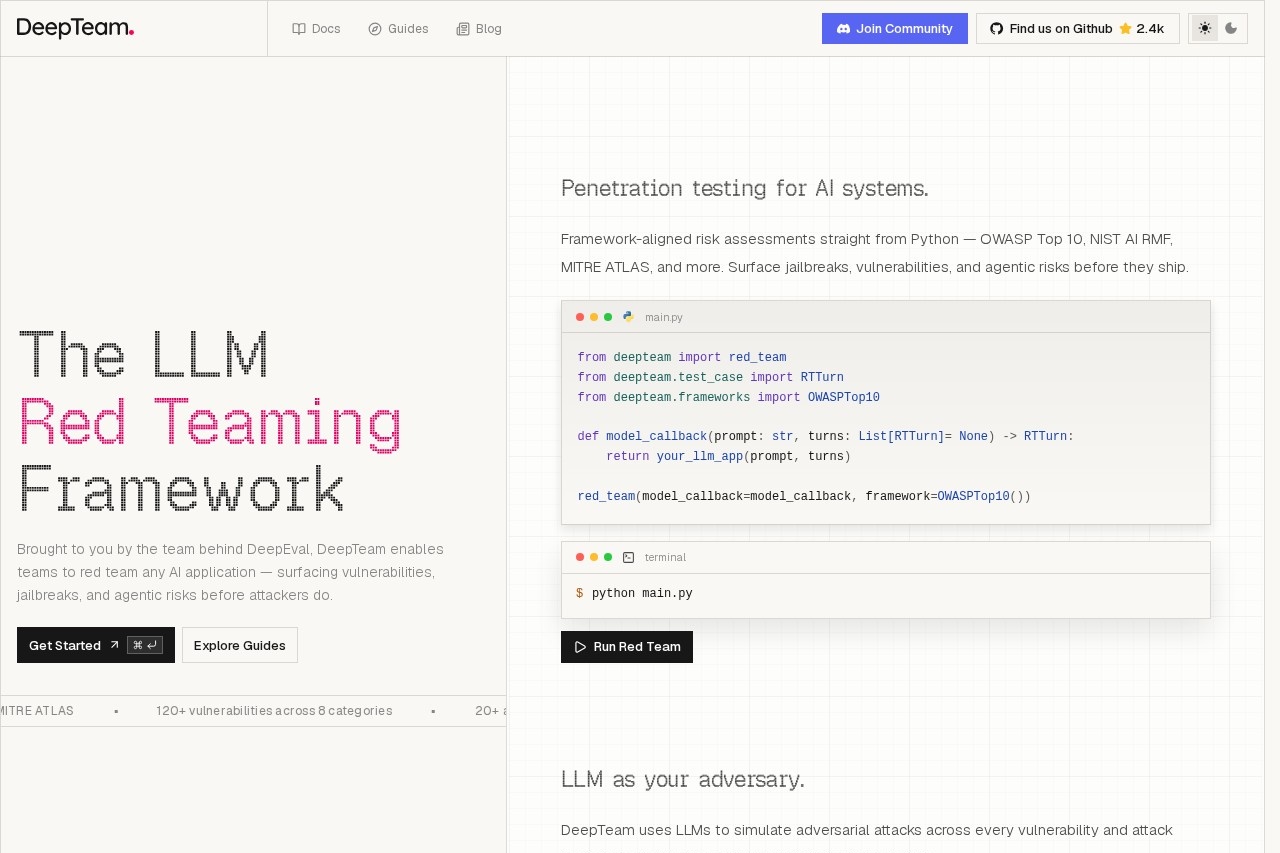
DeepTeam is an open-source LLM red teaming framework for testing and securing LLM applications, covering adversarial attacks, agentic vulnerabilities, guardrails, and compliance frameworks.
Introduction
DeepTeam is an open-source LLM red teaming framework designed to test and secure LLM applications. It helps developers and security teams identify and fix potential vulnerabilities in AI applications, including adversarial attacks, agentic vulnerabilities, guardrail weaknesses, and compliance issues. With DeepTeam, you can proactively discover and mitigate security risks, ensuring your LLM applications are safe and reliable in production.
Key Features
- Adversarial Attack Simulation: Automatically generate adversarial inputs to test the model's resilience against malicious prompts.
- Agentic Vulnerability Detection: Evaluate the safety and reliability of AI agents in complex scenarios to prevent unauthorized actions.
- Guardrail Assessment: Verify that model outputs are safe and compliant, ensuring they align with expected behavior.
- Compliance Framework Integration: Support for major compliance standards such as GDPR, HIPAA, and more, helping you meet regulatory requirements.
Highlights
- Open Source and Free: Fully open source, community-driven, and continuously updated.
- Easy Integration: Rich APIs and CLI tools make it simple to integrate into existing development workflows.
- Comprehensive Coverage: Covers the entire security testing chain from model to application.
- Customizable: Supports custom test cases and strategies to adapt to different business needs.
Who It's For
DeepTeam is ideal for LLM application developers, AI security engineers, DevOps teams, and compliance officers. Whether you are building chatbots, AI assistants, or complex agent systems, DeepTeam helps you ensure the security of your applications and reduce potential risks.