Strix - Autonomous Security for the AI Era
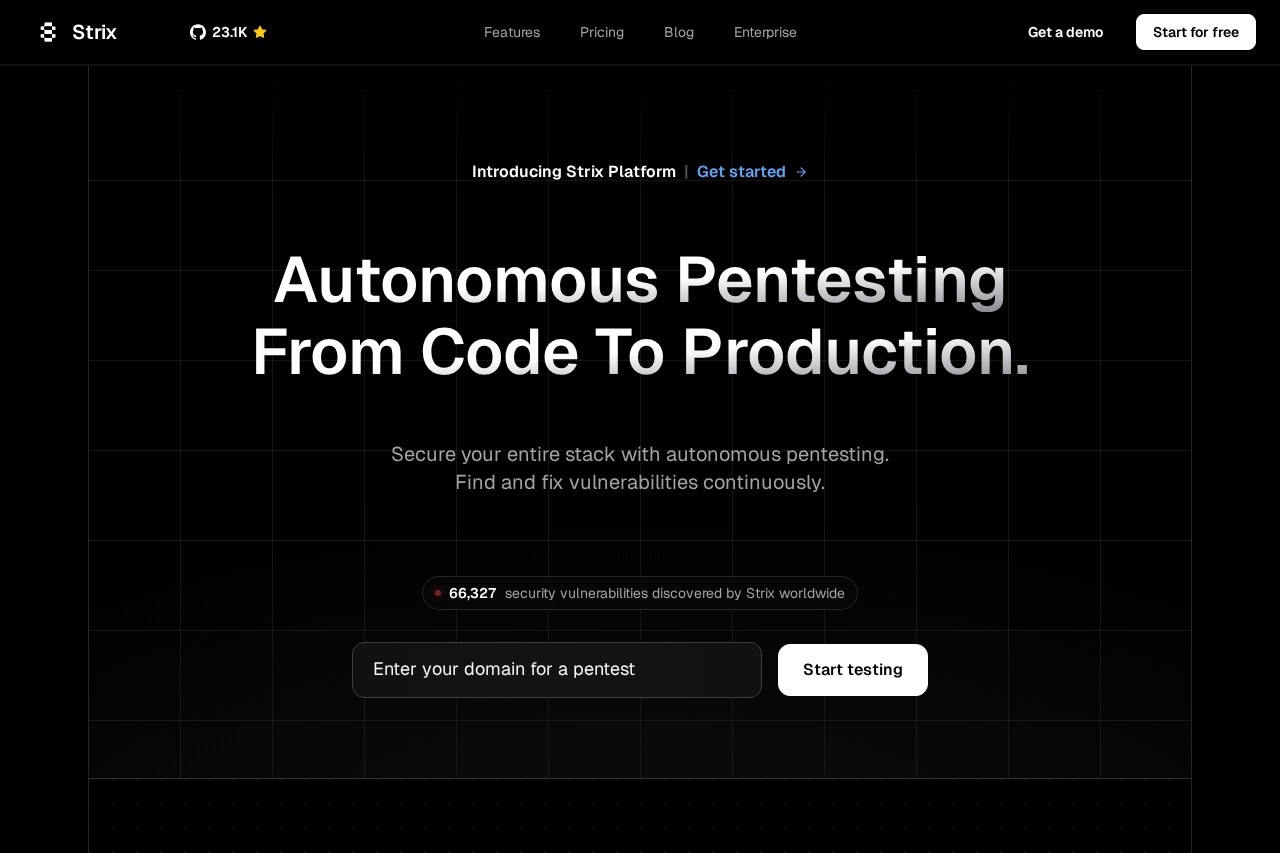
Strix:为 AI 时代而生的自主安全平台
在人工智能与云原生技术飞速发展的今天,传统的安全测试方法已难以应对日益复杂的威胁和快速迭代的开发节奏。Strix 应运而生,它是一个自主安全平台,旨在为现代软件开发生命周期提供全面的自动化安全保障。Strix 能够自动测试代码、API、云环境和基础设施,并直接交付经过验证的发现结果与修复方案,将安全无缝融入 DevOps 流程。
主要功能
Strix 平台提供端到端的安全测试能力,覆盖从开发到部署的各个环节:
- 代码安全测试: 自动扫描源代码,识别潜在的安全漏洞与编码缺陷。
- API 安全测试: 深度检测 API 接口,发现逻辑漏洞、数据泄露等风险。
- 云安全态势管理: 持续监控云资源配置,确保其符合安全最佳实践与合规要求。
- 基础设施即代码扫描: 在部署前检查 Terraform、Kubernetes 配置文件等,防患于未然。
- 自动化修复: 平台不仅发现问题,更能自动生成经过验证的修复拉取请求,帮助团队快速解决问题。
特色优势
Strix 的核心在于其“自主”与“自动化”,为安全团队和开发团队带来革命性的效率提升:
- 验证即结果: 减少误报困扰,交付的每个发现都经过平台验证,直指真正需要处理的风险。
- 修复直达: 直接提供修复代码的 PR,将安全建议转化为可立即执行的操作,极大缩短平均修复时间。
- 全面覆盖: 一个平台整合多项关键安全测试,无需在多个工具间切换,提供统一的安全视图。
- 为 AI 时代构建: 平台设计充分考虑 AI 驱动应用的独特安全挑战,能够适应快速变化的开发模式。
适用人群
Strix 是以下团队和角色的理想选择:
- 开发与 DevOps 团队: 希望将安全左移,在不影响开发速度的前提下,在 CI/CD 管道中自动内嵌安全。
- 安全工程师与 AppSec 团队: 需要高效的工具来扩展其能力,管理大规模、动态环境中的安全风险。
- 云与平台工程团队: 负责维护云基础设施的安全与合规状态,确保基础架构的稳固性。
- 采用 AI 技术的创新企业: 正在构建或部署 AI 应用,需要专门针对新型技术栈的安全保障方案。
常见问题
Q: Strix 如何与现有的 CI/CD 工具集成?
A: Strix 提供丰富的 API 和插件,可以轻松与 Jenkins、GitLab CI、GitHub Actions、CircleCI 等主流工具链集成,实现安全测试的自动化触发。
Q: 自动生成的修复 PR 是否可靠?
A: 是的。Strix 提供的修复方案经过平台验证,确保其有效性和准确性。开发团队可以像审查普通功能代码一样审查并合并这些安全修复。
Q: Strix 主要支持哪些编程语言和云平台?
A: Strix 支持主流编程语言(如 Java, Python, JavaScript, Go 等)和云服务提供商(如 AWS, Azure, Google Cloud)。具体支持列表请参考官方文档。
Q: Strix 适合中小型团队吗?
A: 非常适合。Strix 的自动化特性能够帮助资源有限的团队以极小的开销获得企业级的安全测试能力,是提升安全成熟度的捷径。
English
Strix: The Autonomous Security Platform Built for the AI Era
In today's rapidly evolving landscape of AI and cloud-native technologies, traditional security testing methods are struggling to keep pace with increasingly complex threats and fast-paced development cycles. Strix was created to address this challenge—it's an autonomous security platform designed to deliver comprehensive, automated security assurance across the modern software development lifecycle. Strix automatically tests code, APIs, cloud environments, and infrastructure, delivering verified findings and fixes directly, seamlessly integrating security into your DevOps workflows.
Key Features
The Strix platform provides end-to-end security testing capabilities, covering every stage from development to deployment:
- Code Security Testing: Automatically scans source code to identify potential security vulnerabilities and coding flaws.
- API Security Testing: Deeply inspects API endpoints to uncover logic flaws, data exposure risks, and other vulnerabilities.
- Cloud Security Posture Management: Continuously monitors cloud resource configurations to ensure they align with security best practices and compliance requirements.
- Infrastructure-as-Code Scanning: Proactively checks Terraform, Kubernetes configuration files, and more before deployment to prevent issues before they arise.
- Automated Remediation: The platform doesn't just identify problems—it automatically generates verified fix pull requests, helping teams resolve issues quickly.
Highlights
At the core of Strix is its "autonomous" and "automated" approach, delivering revolutionary efficiency gains for both security and development teams:
- Verified Results: Say goodbye to false positives—every finding delivered by the platform has been validated, pointing directly to the risks that truly need attention.
- Fix-Ready Remediation: Provides fix PRs directly, transforming security recommendations into immediately actionable steps and dramatically reducing mean time to remediation.
- Comprehensive Coverage: Consolidates multiple critical security testing capabilities into a single platform, eliminating the need to switch between tools and providing a unified security view.
- Built for the AI Era: The platform is designed with the unique security challenges of AI-driven applications in mind, capable of adapting to rapidly evolving development patterns.
Who It's For
Strix is the ideal choice for the following teams and roles:
- Development & DevOps Teams: Looking to shift security left and automatically embed security into CI/CD pipelines without compromising development velocity.
- Security Engineers & AppSec Teams: Needing efficient tools to scale their capabilities and manage security risks across large-scale, dynamic environments.
- Cloud & Platform Engineering Teams: Responsible for maintaining the security and compliance posture of cloud infrastructure, ensuring a solid foundation.
- Innovative AI-Driven Enterprises: Building or deploying AI applications and requiring security solutions tailored to new technology stacks.
FAQ
Q: How does Strix integrate with existing CI/CD tools?
A: Strix offers a rich set of APIs and plugins, making it easy to integrate with mainstream toolchains such as Jenkins, GitLab CI, GitHub Actions, and CircleCI, enabling automated security testing triggers.
Q: Are the auto-generated fix PRs reliable?
A: Yes. The fixes provided by Strix are validated by the platform to ensure their effectiveness and accuracy. Development teams can review and merge these security fixes just like they would any regular feature code.
Q: Which programming languages and cloud platforms does Strix support?
A: Strix supports mainstream programming languages (such as Java, Python, JavaScript, Go, etc.) and cloud service providers (such as AWS, Azure, and Google Cloud). Please refer to the official documentation for the complete list of supported technologies.
Q: Is Strix suitable for small and medium-sized teams?
A: Absolutely. Strix's automation capabilities enable teams with limited resources to gain enterprise-grade security testing capabilities with minimal overhead—it's a shortcut to improving security maturity.