
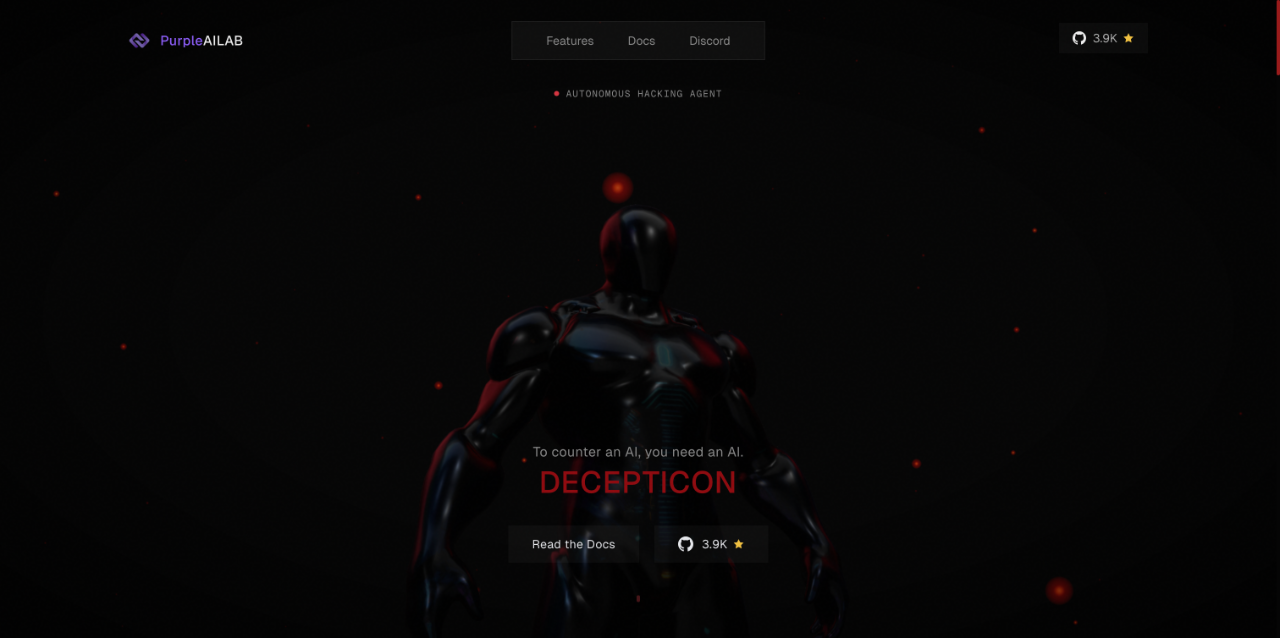
Advanced deception technology by PurpleAILAB. Autonomous hacking agent that turns attackers into intelligence sources.
About
Decepticon is an autonomous hacking agent developed by PurpleAILAB, focused on advanced deception technology. The tool pushes proactive defense to a new level — instead of passively waiting for attacks to happen, it actively lures intruders in and turns them into valuable sources of intelligence. Decepticon simulates vulnerable points commonly found in real network environments, such as databases, API endpoints, or authentication services. Once an attacker triggers a trap, the system automatically records their behavior patterns, toolchains, and attack intent. Powered by an AI-driven analysis engine, Decepticon classifies threat levels in real time and delivers actionable insights to security teams, helping organizations counter threats in the early stages of an attack.
Key Features
Pricing & Fees
- Pricing: Three plans are listed: Free Preview at $0, Solo at $19/month, and Pro at $39/month. New Solo and Pro purchases are currently closed and require a purchase request.
- Free tier: The Free Preview requires no card and includes a guided sample engagement, sample findings, evidence, and reports, plus cached public program discovery.
- Plan limits: Solo includes 12 active runtime hours monthly and 1 concurrent agent run; Pro includes 24 runtime hours, 2 concurrent agent runs, and 3 workspace members.
- Model usage: Bring your own model key (charges billed by your provider), or optionally buy managed credit packs separately; credits do not expire.
- Self-hosted: A $0 platform fee option to run the open-source agent system on your own infrastructure, handling isolation, upgrades, and model keys yourself.
Who It's For
Red teams and penetration testers can use Decepticon to build realistic honeypot networks and simulate complex attack scenarios to validate defense systems. Enterprise security operations teams can proactively detect latent threats and reduce the time attackers spend inside the network. Threat intelligence analysts gain first-hand attacker behavior data that supplements external intelligence sources and improves early warning accuracy. CISOs and security management leaders can leverage quantified intelligence reports to demonstrate the tangible impact of security investments and evolving attack trends to the board.
Related Tutorials
View all →
Related Tools
View all → Yuxi - RAG Harness for AI Agents Yuxi provides a RAG harness to enhance AI agents with retrieval-augmented generation capabilities.
 omp - A Coding Agent with the IDE Wired In Oh My Pi (omp) is a coding agent that integrates with your IDE, leveraging LSP and DAP for seamless development. Built in Rust for performance.
 DeepEval by Confident AI - LLM Evaluation Framework Open-source LLM evaluation framework with 50+ plug-and-play metrics for AI agents, RAG, chatbots, and more.
 OmniRoute - Free AI Gateway for Multi-Provider LLMs Free, open-source AI router with auto-fallback. 236 providers, one endpoint, 95 MCP tools, 17 routing strategies, A2A protocol, auto-combo engine, semantic cache, memory & skills. Deploy anywhere.
 AgentsView - AI Agent Session Manager Local-first desktop and web app for managing AI agent sessions.